DBS combines machine learning with deliberate pauses in Singapore’s scam defence
DBS describes a layered anti-scam service. The analysis examines how a risk signal becomes an understandable intervention and recovery.
The fastest payment is not always the safest payment. A person being coached by a scammer may want a transfer completed immediately, even while a bank's systems detect that something is unusual. That makes scam prevention a demanding banking application for AI: identifying a suspicious pattern is only the beginning. The service must decide how to interrupt, how to communicate and how to help the customer establish what is happening.
In its [2025 chief risk officer statement](https://www.dbs.com/annualreports/2025/cro-statement.html), DBS reports a 35% increase in scam saves during the year. The same account describes stronger AI and machine-learning models for detecting mule accounts, payment-journey pauses and other controls. These are bank-reported results from a combination of measures. They do not establish that AI alone caused the improvement or reveal a model's false-positive rate. Sources were checked on 16 October 2026.
Detection is part of a layered service
The [DBS Sustainability Report 2025](https://www.dbs.com/annualreports/2025/i/pdf/DBS_SR2025.pdf), in its customer-protection discussion, describes a fraud-detection system using machine learning alongside a rule-based surveillance engine. It says lower-risk cases can trigger notifications intended to make customers pause, while higher-risk cases can lead to a delay or hold and contact for verification. It also describes a round-the-clock Anti-Scam Team. That is an account of operational design, not a promise that every fraudulent transfer will be stopped.
The combination is important. A predictive model can identify a pattern that deserves attention. A rule can impose a particular safeguard. A specialist can ask questions that a score cannot resolve. A customer-facing message can create time to reconsider an instruction. Describing all of those as an AI success would obscure the different contributions, and make it harder to identify what needs improving when an intervention does not work.
Equally, an unusual transaction is not proof that a customer has been deceived. People make legitimate payments that differ from their routine. A protective hold can therefore create a service problem even when the underlying aim is sound. The bank needs a useful path for resolving a genuine transfer as well as a way to stop a suspicious one. That balance is an analytical requirement of the service problem, not a finding about an individual DBS case.
Singapore gives the intervention an institutional setting
The policy context helps explain why banks are building layers rather than relying on warnings alone. In its [24 October 2024 announcement](https://www.mas.gov.sg/news/media-releases/2024/mas-and-imda-announce-implementation-of-shared-responsibility-framework-from-16-december-2024), MAS and IMDA set 16 December 2024 as the implementation date for the Shared Responsibility Framework. They also described an additional financial-institution duty for real-time surveillance of unauthorised phishing transactions that drain accounts, with a six-month transition for that duty. These are dated framework details, not a blanket promise of reimbursement for every scam.
The [MAS explanation of the framework](https://www.mas.gov.sg/regulation/combatting-scams) says it assigns relevant duties to financial institutions and telecommunications providers and sets expectations for payouts where those duties are breached. Scope matters: the framework concerns defined phishing scams. A reader should not infer that every authorised payment, investment deception or other fraud falls within it. An affected customer's circumstances require the bank's actual investigation, not an article's diagnosis.
Authentication is another distinct layer. A [9 July 2024 MAS and Association of Banks in Singapore announcement](https://www.mas.gov.sg/news/media-releases/2024/banks-in-singapore-to-strengthen-resilience-against-phishing-scams) described major retail banks phasing out login one-time passwords for digital-token users. The aim was to reduce phishing exposure. This is not the same technology as transaction-risk scoring, and neither layer should be mistaken for complete protection against social engineering. The cited announcement describes its specified rollout population and timing, not every current account configuration.
For the customer, these layers may appear as friction: an extra confirmation, a delay or a request to speak with the bank. A system can be technically effective yet difficult to understand. Clear language should explain the immediate state of the payment and the safe route for assistance, without revealing sensitive detection details. The customer should not have to decide which part was a model, a rule or a staff judgement to know what to do next.
The workforce task becomes investigation and communication
The bank's account of a dedicated team points to a part of the work that headline AI discussions can miss. A suspicious transfer may involve an anxious customer who is still receiving instructions from someone else. Staff must establish a trusted conversation and interpret the surrounding circumstances. A model's risk indication can support that work, but it does not create empathy, establish identity or settle the facts by itself.
Teams also need information about legitimate interruptions. A customer may need to pay an urgent invoice or help a family member. The service should preserve an intelligible record of what was delayed, what the customer was told and how it was resolved. Reviewing those cases can reveal whether the intervention is proportionate and accessible. This is a proposed evaluation focus, not a claim that the public sources quantify customer inconvenience or staff time.
The reported increase in scam saves should therefore be read alongside unanswered questions. What precisely was counted? How did the bank distinguish prevention from recovery? Did the underlying volume and type of scam attempts change? The selected public statements do not provide enough detail to calculate a causal contribution for each control. This article does not turn the reported percentage into an AI accuracy rate, a monetary return or a comparison with another bank.
A proposed learning exercise: protect a payment without accusing the payer
An original workshop could use synthetic payment journeys to practise intervention and recovery. One scenario represents an ordinary but unusual supplier payment; another represents an invented customer being pressured by an impersonator. The examples would use no live account, production risk threshold or real scam victim. The learning objective is to explain a protective interruption while keeping the facts and uncertainty clear.
Participants review a proposed notification before discussing the model score. Does it say what has happened to the payment? Does it offer a safe way to contact the bank? Does it avoid calling the customer fraudulent or telling them that the transfer is definitely a scam? The team can compare a vague warning with a carefully written explanation and ask which lets a person take a meaningful next step without exposing operational detection logic.
A second group plays the receiving specialists. They work from a minimal synthetic case record and practise recording the customer's explanation without treating it as independently established. They also examine a correction: the customer supplied a mistaken detail and now needs to change it. A useful workflow should preserve the original report and the correction, rather than silently rewriting the case into a misleadingly clean history.
Finally, learners trace the recovery path for the legitimate payment. They identify what must be verified, who can release an interruption and what the customer sees afterwards. This is where a demonstration of detection becomes a service-design exercise. Success means a defensible decision and understandable continuation, not merely a colourful dashboard with a risk score or a claim that the software has prevented a loss.
DBS's reporting provides a real example of machine learning operating within a larger anti-scam system. Singapore's framework adds a concrete allocation of responsibilities around particular phishing losses. Together they show why practical banking AI depends on the actions surrounding a prediction. A well-timed pause can matter, but so can the quality of the conversation that follows it and the route back to ordinary banking when the concern is resolved.
Explanatory diagram and accessible reading guide
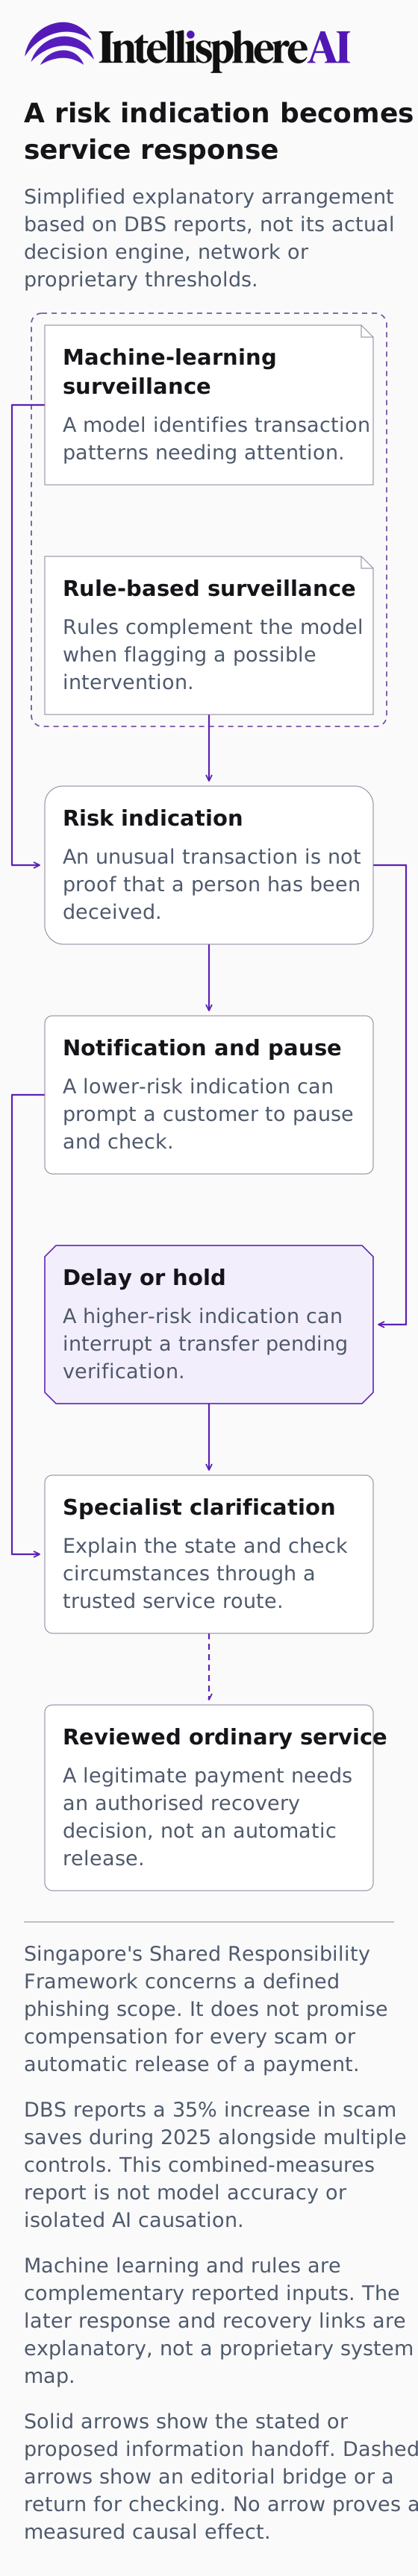
*Original educational infographic based on attributed reports and a fictional proposed exercise; not the named bank’s internal architecture, actual customer decision or measured result.*
[Open the full-size explanatory diagram](/assets/bank-singapore-risk-response-20261016.svg)
This original diagram explains attributed source context and a fictional learning exercise. The exercise has not been run; the diagram is not an authentic product interface, internal bank architecture or measured operational result.
A risk indication becomes a service response
Simplified explanatory arrangement based on DBS reports, not its actual decision engine, network or proprietary thresholds.
Machine-learning surveillance
A model identifies transaction patterns needing attention.
Rule-based surveillance
Rules complement the model when flagging a possible intervention.
Risk indication
An unusual transaction is not proof that a person has been deceived.
Notification and pause
A lower-risk indication can prompt a customer to pause and check.
Delay or hold
A higher-risk indication can interrupt a transfer pending verification.
Specialist clarification
Explain the state and check circumstances through a trusted service route.
Reviewed ordinary service
A legitimate payment needs an authorised recovery decision, not an automatic release.
Singapore's Shared Responsibility Framework concerns a defined phishing scope. It does not promise compensation for every scam or automatic release of a payment.
DBS reports a 35% increase in scam saves during 2025 alongside multiple controls. This combined-measures report is not model accuracy or isolated AI causation.
Machine learning and rules are complementary reported inputs. The later response and recovery links are explanatory, not a proprietary system map.
Solid arrows show the stated or proposed information handoff. Dashed arrows show an editorial bridge or a return for checking. No arrow proves a measured causal effect.
Reported model surveillance contributes an indication for review.
Reported rules complement the indication.
A lower-risk case can receive a notification or pause.
A higher-risk case can be delayed or held.
A customer needing help can reach specialist clarification.
A held or delayed payment needs verification and explanation.
The fictional exercise traces authorised recovery for a legitimate payment.
Diagram source references
- [S17: CRO statement | DBS Bank](https://www.dbs.com/annualreports/2025/cro-statement.html) — DBS.
- [S18: DBS Sustainability Report2025](https://www.dbs.com/annualreports/2025/i/pdf/DBS_SR2025.pdf) — DBS.
- [S21: Banks in Singapore to Strengthen Resilience Against Phishing Scams](https://www.mas.gov.sg/news/media-releases/2024/banks-in-singapore-to-strengthen-resilience-against-phishing-scams) — Monetary Authority of Singapore / named joint issuer.
- [S22: MAS and IMDA Announce Implementation of Shared Responsibility Framework from16December2024](https://www.mas.gov.sg/news/media-releases/2024/mas-and-imda-announce-implementation-of-shared-responsibility-framework-from-16-december-2024) — Monetary Authority of Singapore / named joint issuer.
- [S23: Combatting Scams](https://www.mas.gov.sg/regulation/combatting-scams) — Monetary Authority of Singapore / named joint issuer.